ICS Compute × CrowdStrike
CrowdStrike Falcon. Built for Modern Threat Defense.
ICS Compute helps organizations implement and integrate CrowdStrike security capabilities across endpoints, cloud environments, and security operations.
Discuss Your Security EnvironmentSecurity environmentSelect an area
- EndpointDevice and process activity
- CloudWorkload and configuration signals
- IdentityAuthentication and access behavior
- DetectionSignals from each area correlated for investigation
The Falcon Platform
One Platform. Multiple Layers of Defense.
CrowdStrike Falcon connects security capabilities across endpoints, cloud workloads, identities, and threat detection.
Endpoint detectionFull size ↗
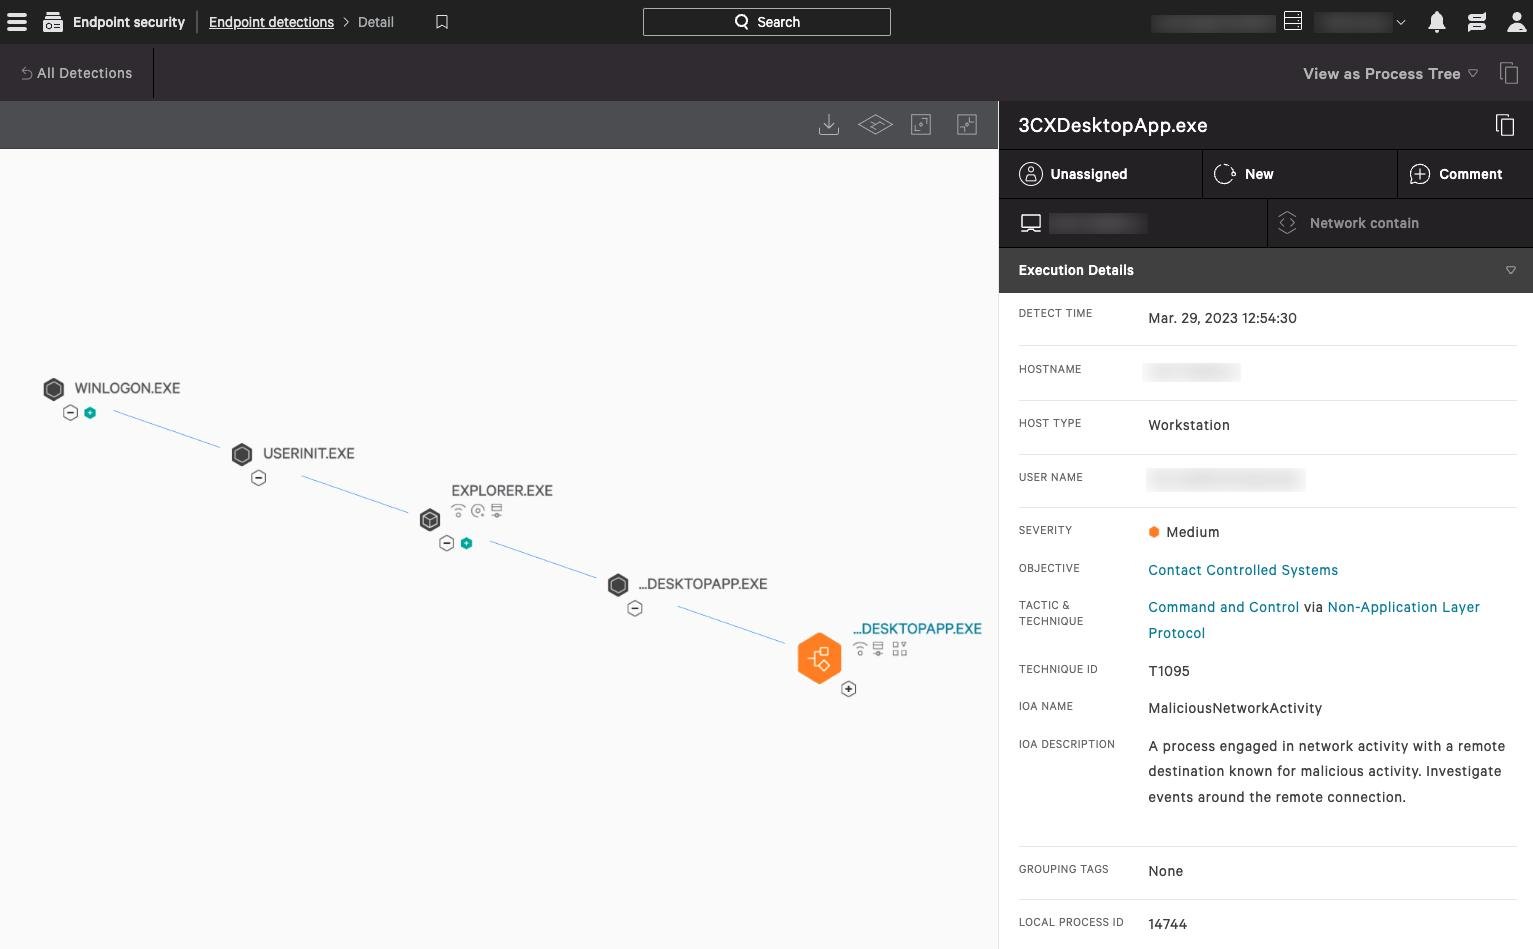
- The process tree shows the launch chain: winlogon.exe, userinit.exe, explorer.exe, then 3CXDesktopApp.exe.
- The flagged process is highlighted; the panel lists severity, MITRE ATT&CK technique T1095, and why it was flagged.
- Response starts from the same view, for example containing the host from the network.
Cloud & application postureFull size ↗
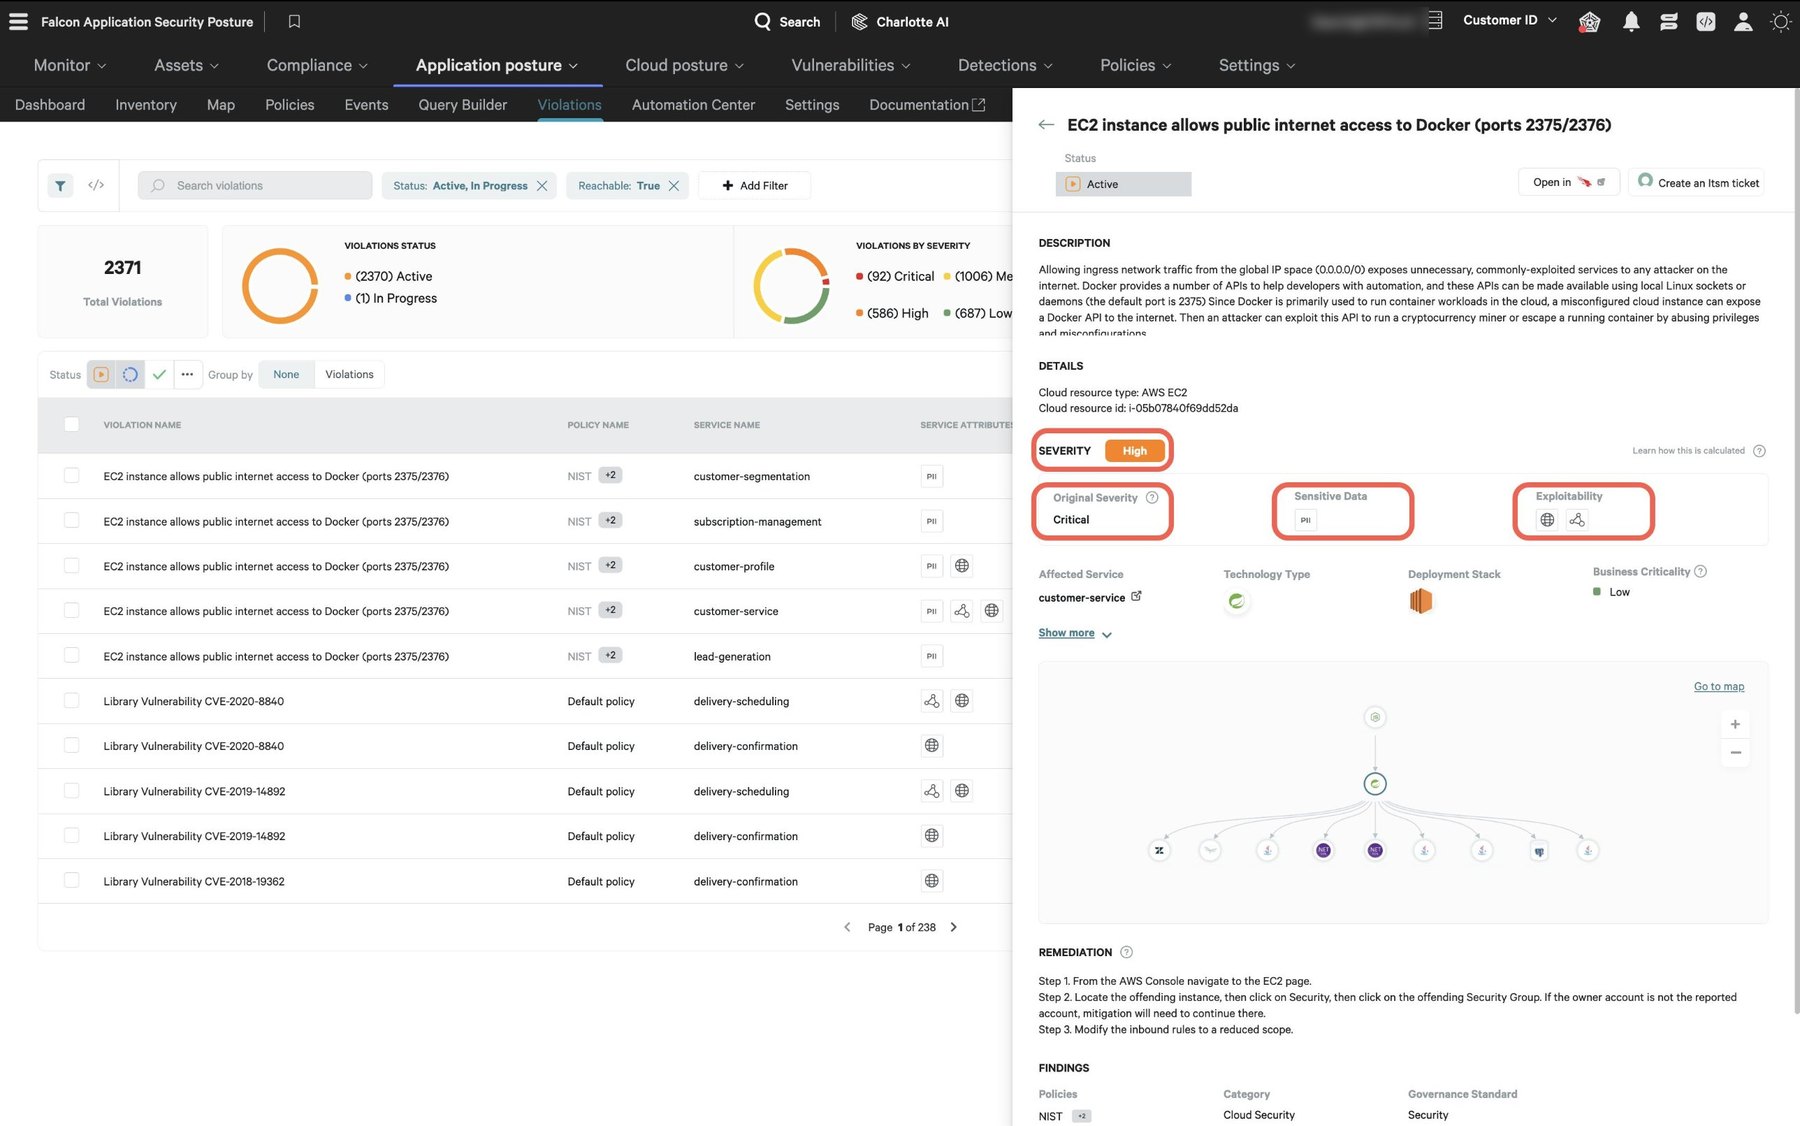
- A list of posture violations across services, with status and severity counts.
- The selected finding: an AWS EC2 instance exposes the Docker API (ports 2375/2376) to the internet.
- The detail panel shows severity, affected service, and step-by-step remediation.
Identity protectionFull size ↗
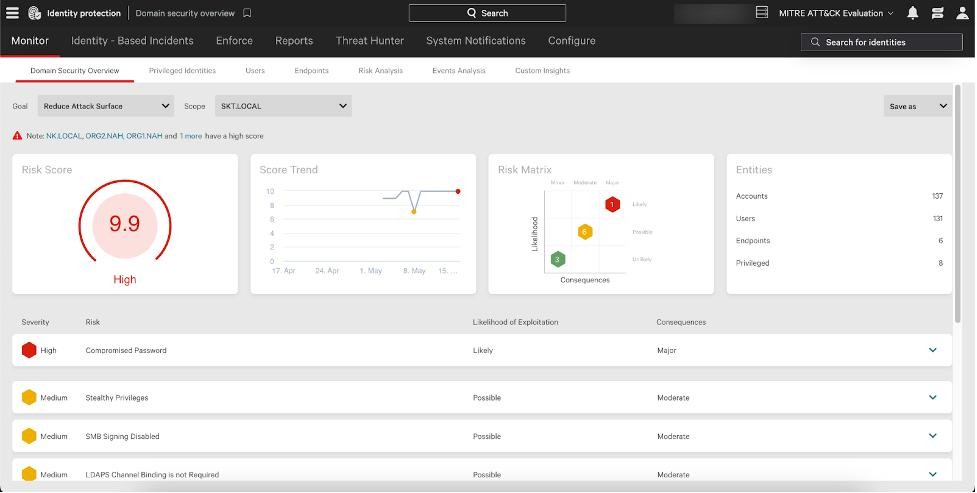
- A domain-level risk score and trend for the Active Directory environment.
- A risk matrix that weighs likelihood of exploitation against consequences.
- Prioritized identity risks, such as a compromised password or SMB signing disabled.
Detection investigationFull size ↗
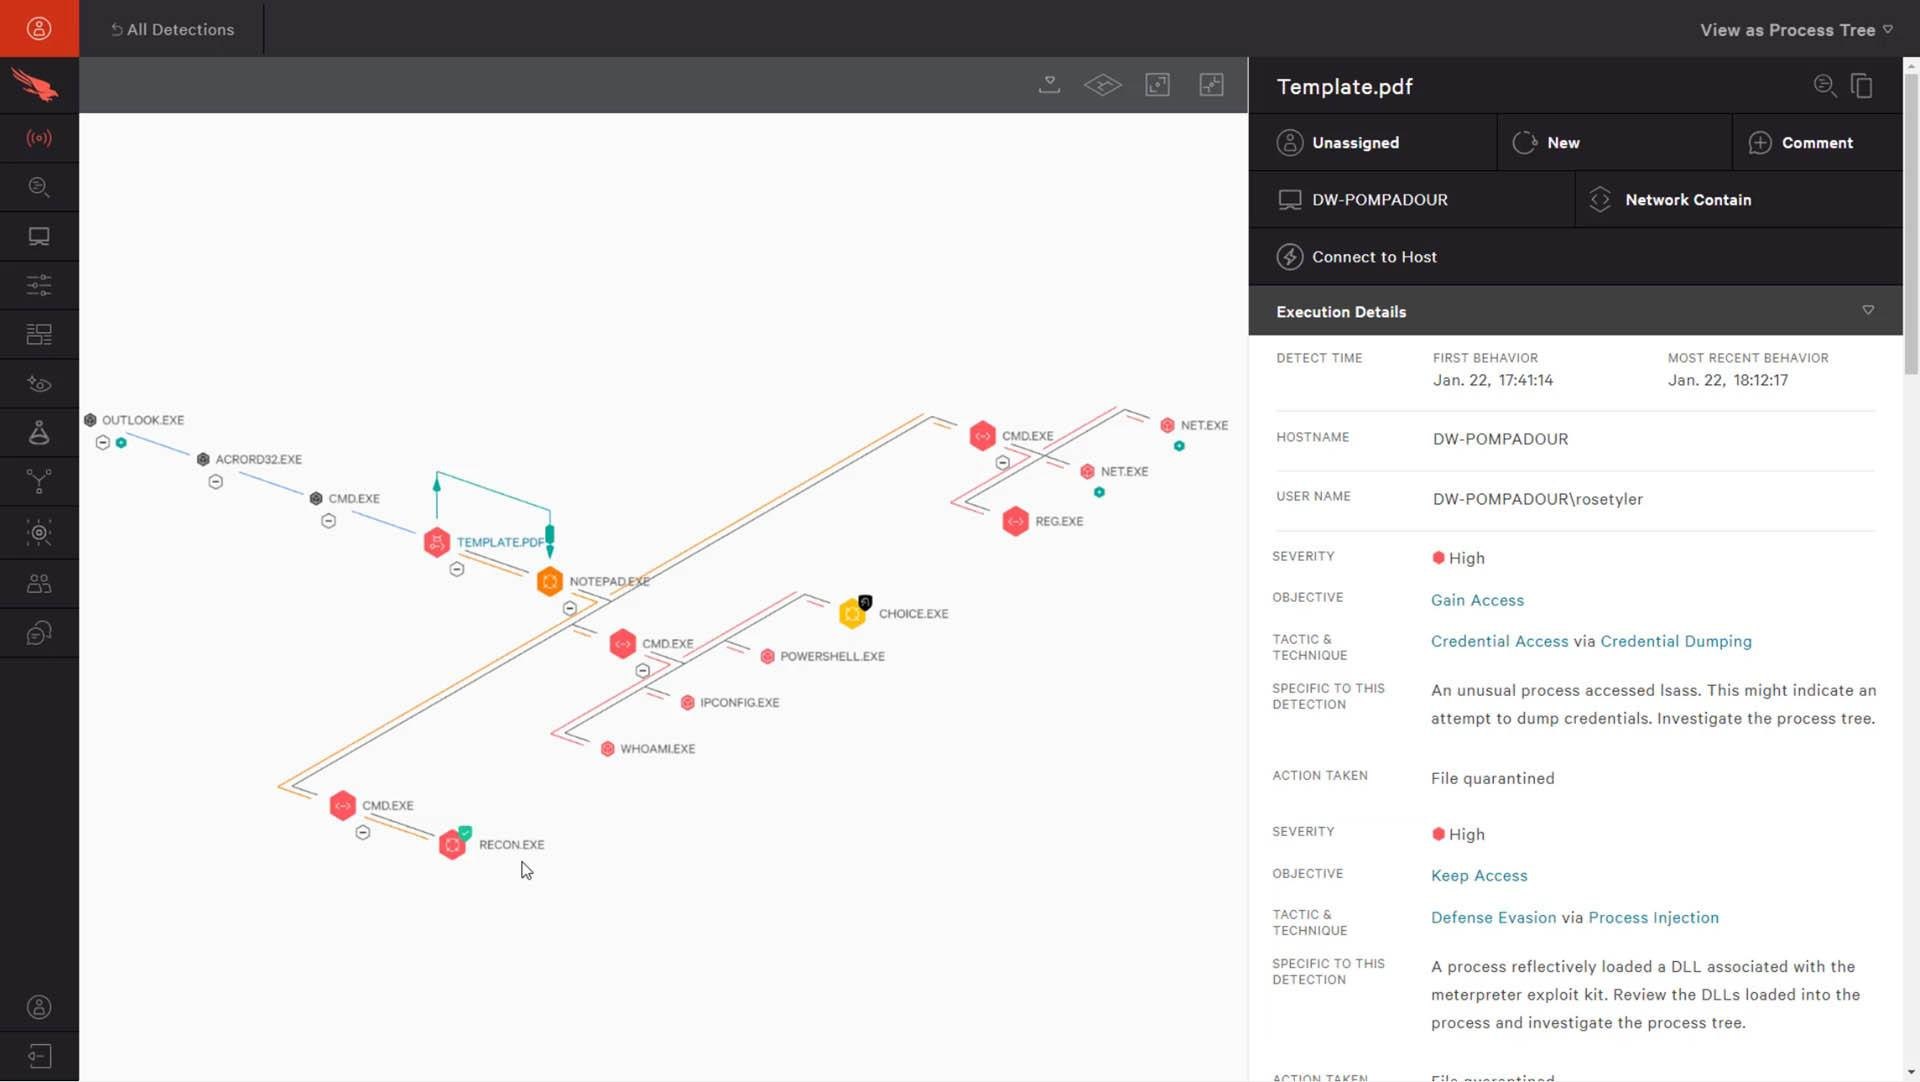
- A PDF opened from email (Outlook, then Acrobat) launches a chain of follow-on commands on one host.
- Related behaviors, including credential dumping and process injection, appear in a single detection.
- The panel shows tactics, techniques, actions taken (file quarantined) and response options.
Screenshots show the CrowdStrike Falcon console. Available capabilities depend on the Falcon modules and entitlements in each deployment.